SSL Certificate Guidance
Introduction
Biza uses TLS certificates to ensure secure communication between its services. As a HaaS customer, the specific requirements for TLS certificates depend on the configuration and implementation features. In some cases, you may need to provide Certificate Signing Requests (CSRs) or pre-issued certificates to Biza. For further general information on TLS certificates, please see the following documentation.
TLS Certificates
There are four categories of TLS certificates utilised by Biza.
- Public server
- ACCC server
- Internal server
- Internal client (mTLS)
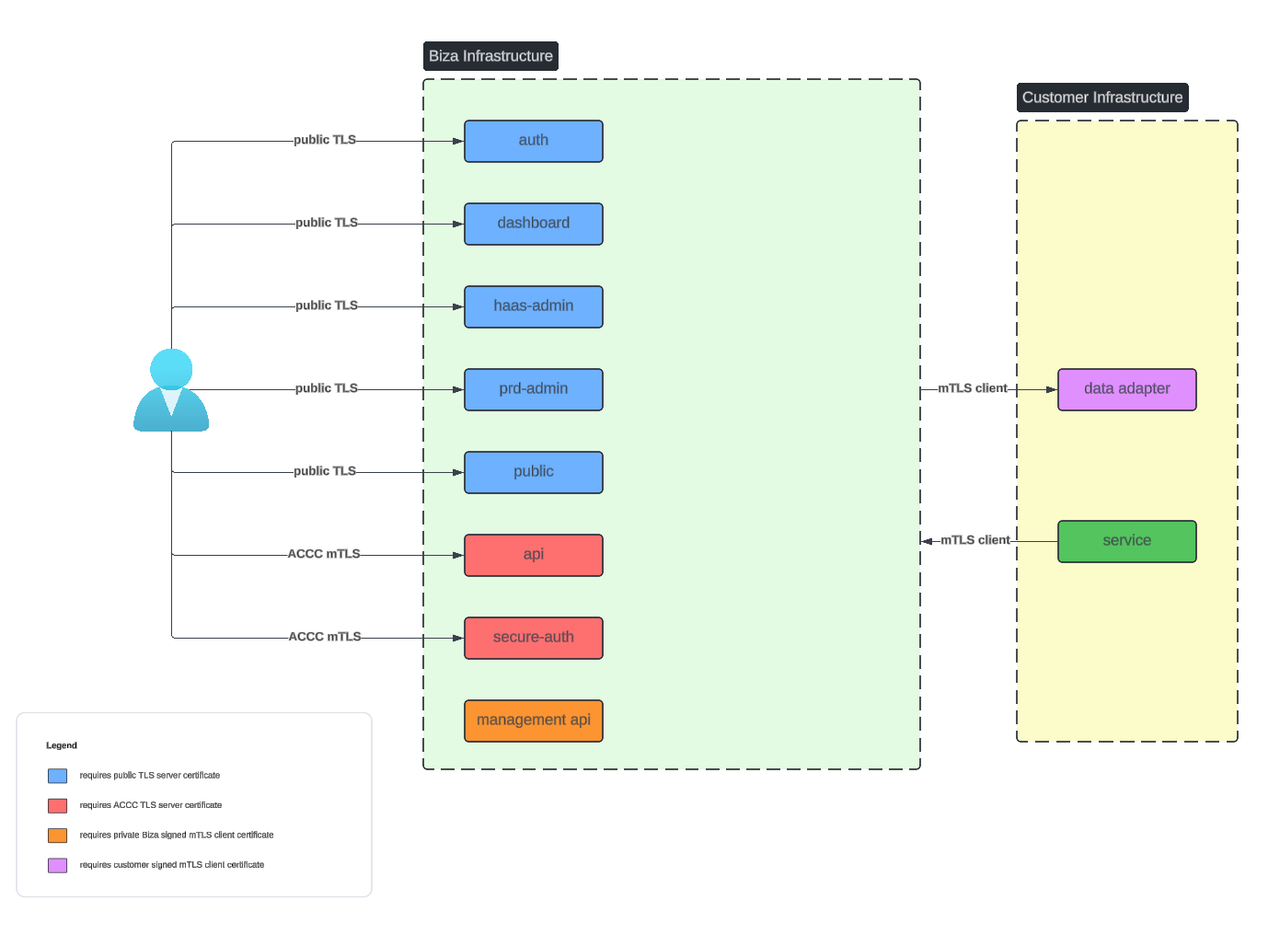
SSL Infrastructure
Public TLS Certificates
Public TLS certificates secure internet-accessible endpoints using certificates signed by trusted public Certificate Authorities (CAs) included in default trust stores. These certificates are automatically trusted by most computers and browsers.
Delegated DNS to Biza
If you have delegated DNS management to Biza, no action is required on your part. Biza will handle TLS certificate provisioning, including Domain Control Validation (DCV), to secure your endpoints.
Non-Delegated Domains
If DNS management is not delegated to Biza, we will provide CSRs for you to submit to your chosen public certificate provider to obtain the required certificates. Once the certificates are issued and returned to Biza, we will install them.
The domains typically requiring public TLS certificates are:
| Domain | Purpose | Type |
|---|---|---|
| auth.cdr.customer.domain | Authentication | Public SSL |
| dashboard.cdr.customer.domain | Consumer Dashboard | Public SSL |
| public.cdr.customer.domain | Public Data | Public SSL |
ACCC Server Certificates
ACCC server certificates are issued by the ACCC CDR authority and are used to secure communication between recipients and holders for specific services that only recipients can access.
These certificates are only used for Production spaces during Conformance Test Suite (CTS) verification, which is typically conducted in the customer staging space. In non-production spaces, Biza uses its own certificate authority to sign certificates that are valid for the Biza Test Registry, and there is no action required by the customer.
Regardless of whether DNS is delegated to Biza, production spaces will require certificates obtained from the ACCC portal by submitting CSRs that BIza generates and provides to customers.
The domains that typically require ACCC Private CA TLS certificates are:
| Domain | Purpose | Endpoint |
|---|---|---|
| api.cdr.customer.domain | API Endpoints | ACCC Private CA |
| secure-auth.cdr.customer.domain | Secure Authentication for Recipients | ACCC Private CA |
Internal Server and Client
Data Adapter Internal Client
For customers choosing to secure their data adapter with mutual TLS (mTLS), signed client-side certificates must be provided that allows Biza to access your data adapter. Biza will generate and provide a CSR for signing by your Certificate Authority, which Biza will then use to securely communicate with your data adapter.
Further, if you choose to use a server certificate for the data adapter signed by a private CA, you will need to provide Biza with the CA chain of trust to ensure that your server data adapter certificate is recognised as valid.
Management API Internal Server and Client
For customers requiring Management API access, you will need to provide a CSR so Biza can return a signed client certificate. This certificate will allow you to access your space's Management API.