Biza Managed
This page describes the Biza Managed One-Time-Password (OTP) method of Authentication.
The Biza Managed (BM) method is an authentication mechanism whereby Biza is responsible for OTP generation, delivery, and verification of the customer's details. This mechanism introduces implicit trust as Biza can directly enumerate Principals based on Username fields.
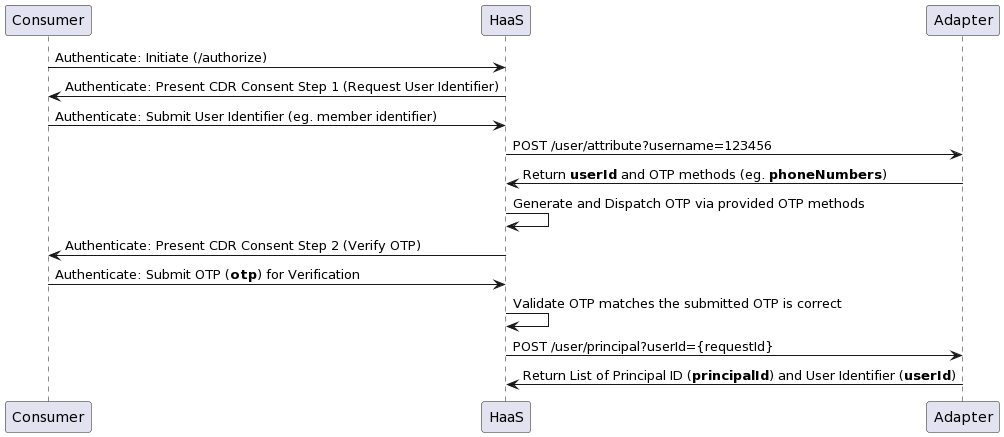
The Biza Managed method is completed in the following sequence:
- Get Username Attributes: The Username (
username) is accepted via the Data Adapter and a unique User Identifier (userId) and methods for OTP receipt (mobile and/or email) is returned.
If getUsernameAttributes returns a mobile number, it will take precedence over an email and Biza Managed OTP will send an SMS via the Telstra Gateway. We recommend the data adapter
return either a mobile number or an email address to keep the OTP delivery consistent for users.
To enable both Biza Managed and Customer Managed email-based OTP via SendGrid, the getUserNotificationInfo data adapter endpoint must be implemented. Further, the email OTP delivery mechanism must be the same as the ones used for Notifications.
- OTP Generation and Dispatch: After processing the OTP receipt methods the HaaS generates an OTP and dispatches it to the User.
- OTP Verification: The OTP received by the User is verified and the previously obtained
userId(from Get Username Attributes) is retrieved. - Get User Principals: The
userIdand the OTP (otp) submitted by the User are received. The API returns a list of Principal Identifiers (principalIds) and a singleuserId.
Advantages
- Lower implementation required as the Adapter implementation is a simplified lookup.
- Biza manages the delivery of SMS messages via its Enterprise SMS Gateway (Telstra).
- Email based OTPs are delivered via the agreed Send Notification API method or via SendGrid.
- HaaS Manager can assist administrators by being able to lookup Users and Principals by their login attributes. This is useful when these IDs are not known by CDR support staff.
Disadvantages
- User Identifiers are disclosed directly if the username is known.
- Principal Identifiers are disclosed directly using User Identifiers.
- Currently, no explicit method of returning Ineligible Block information. This is a deliberate design decision to protect this method from enumeration attacks but means that the method for presentation is limited to a consent flow that simply states "No Eligible Accounts".
While a low risk, if the username is an incrementing member identifier, or otherwise easily determined, this method could potentially be exposed to an enumeration attack.
High Level UML Diagram
Click here for the data-adapter endpoint configuration.