Vulnerability
Customer vulnerability, and the means with which to manage it, is a complex topic that is intertwined between the DSB Standards and the CDR Rules.
Vulnerability status is discovered either using the Data Adapter or centrally managed in HaaS Manager.
Vulnerability status is represented as a simple true/false boolean as HaaS does not require knowledge of the reason for the status.
Notifications
Notification behaviour changes based on the vulnerability status of related parties.
For Consumers who are considered vulnerable, all other parties will not receive notifications. In essence, a vulnerable party is treated as if they were a single user.
For Consumers for which a related party is identified as vulnerable, all parties will receive notifications.
Configuration
The vulnerability status source is determined based on the authoritative_source_vulnerable_status configuration setting:
| Value | Source of Vulnerability Flag |
|---|---|
| WIKKIT_GATE | HaaS Manager |
| DATA_ADAPTER | Get User API vulnerable attribute List Accounts accountCustomers[].vulnerable if check-upstream-accounts-for-vulnerability is enabled. |
HaaS Manager
Administering vulnerability status from HaaS Manager allows for CDR vulnerability to be managed as a standalone functionality from upstream data sources.
Refer to View Vulnerable Customers and Manage a Vulnerable Status from the HaaS Administration guide.
Adapter
There are multiple Data Adapter endpoints which are used to communicate vulnerability status.
Get User
The Get User endpoint is used to communicate the current Consumers vulnerability status.
Refer to Get User API endpoint and guidance.
List Accounts
The List Accounts endpoints for multiple industries contain an attribute accountCustomers which is used to describe the relationships of account holders and those with access. Vulnerability status of related Consumers facilitates behaviour change for non-vulnerable parties.
Refer to List Banking Accounts or List Energy Accounts endpoint and guidance.
Consent Behaviour
When a Consumer is identified as vulnerable the consent flow behaviour is altered, notably a notification that other account holders will not be notified.
Once arrangements are established they are stored with a privacy attribute (private) that persists regardless of a change of the current vulnerability.
There is no explicit guidance regarding the behaviour of existing arrangements when a vulnerability flag has been removed. Currently, the HaaS retains private status of arrangements established during a period of vulnerability.
Arrangements which are amended inherit the current status of the user amending them. That is, even if they were private to begin with, during amendment if the user does not retain vulnerable status the arrangement is updated to have a false private value.
Users with a vulnerability flag applied are able to share data, as if a sole account owner, regardless of the Disclosure Option specified.
Vulnerability does not prevent data sharing
A vulnerability flag never blocks the creation of a data sharing arrangement. It only changes behaviour:
- Notifications to other parties are suppressed.
- Arrangements created by a vulnerable Consumer are stored as
privateand the vulnerable Consumer is treated as a sole account owner (joint-account approval steps are bypassed), regardless of the Disclosure Option.
This applies across party types. Where an account holder is vulnerable, a Secondary User is still able to establish a data sharing arrangement for that account. Vulnerability is evaluated for the Consumer performing the action, in the context of related parties — it is not a barrier to sharing for any other party.
See Secondary Users — Account Holder Restrictions for further detail.
Confirmation Screen
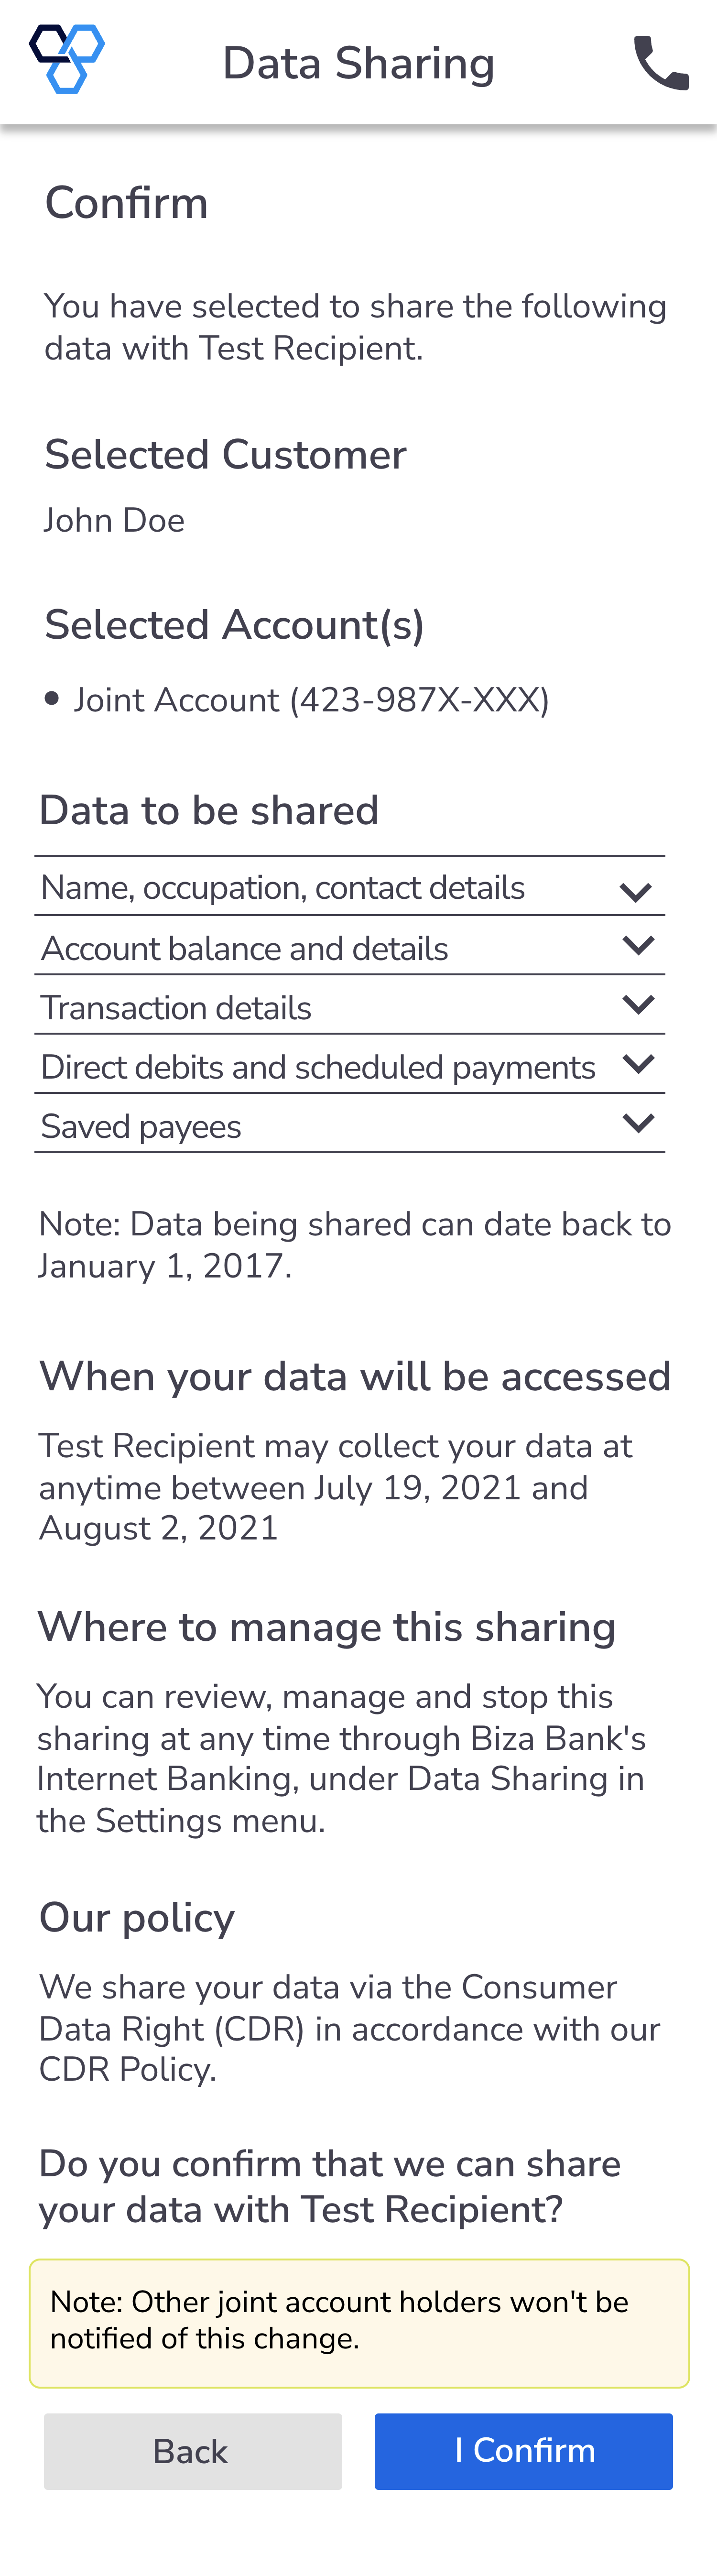
Confirm Data Sharing
Consumer Dashboard Behaviour
When an arrangement has a private status, meaning it has been established when the customer vulnerable value was true the cancellation of arrangements explicitly states that notifications will not be sent.
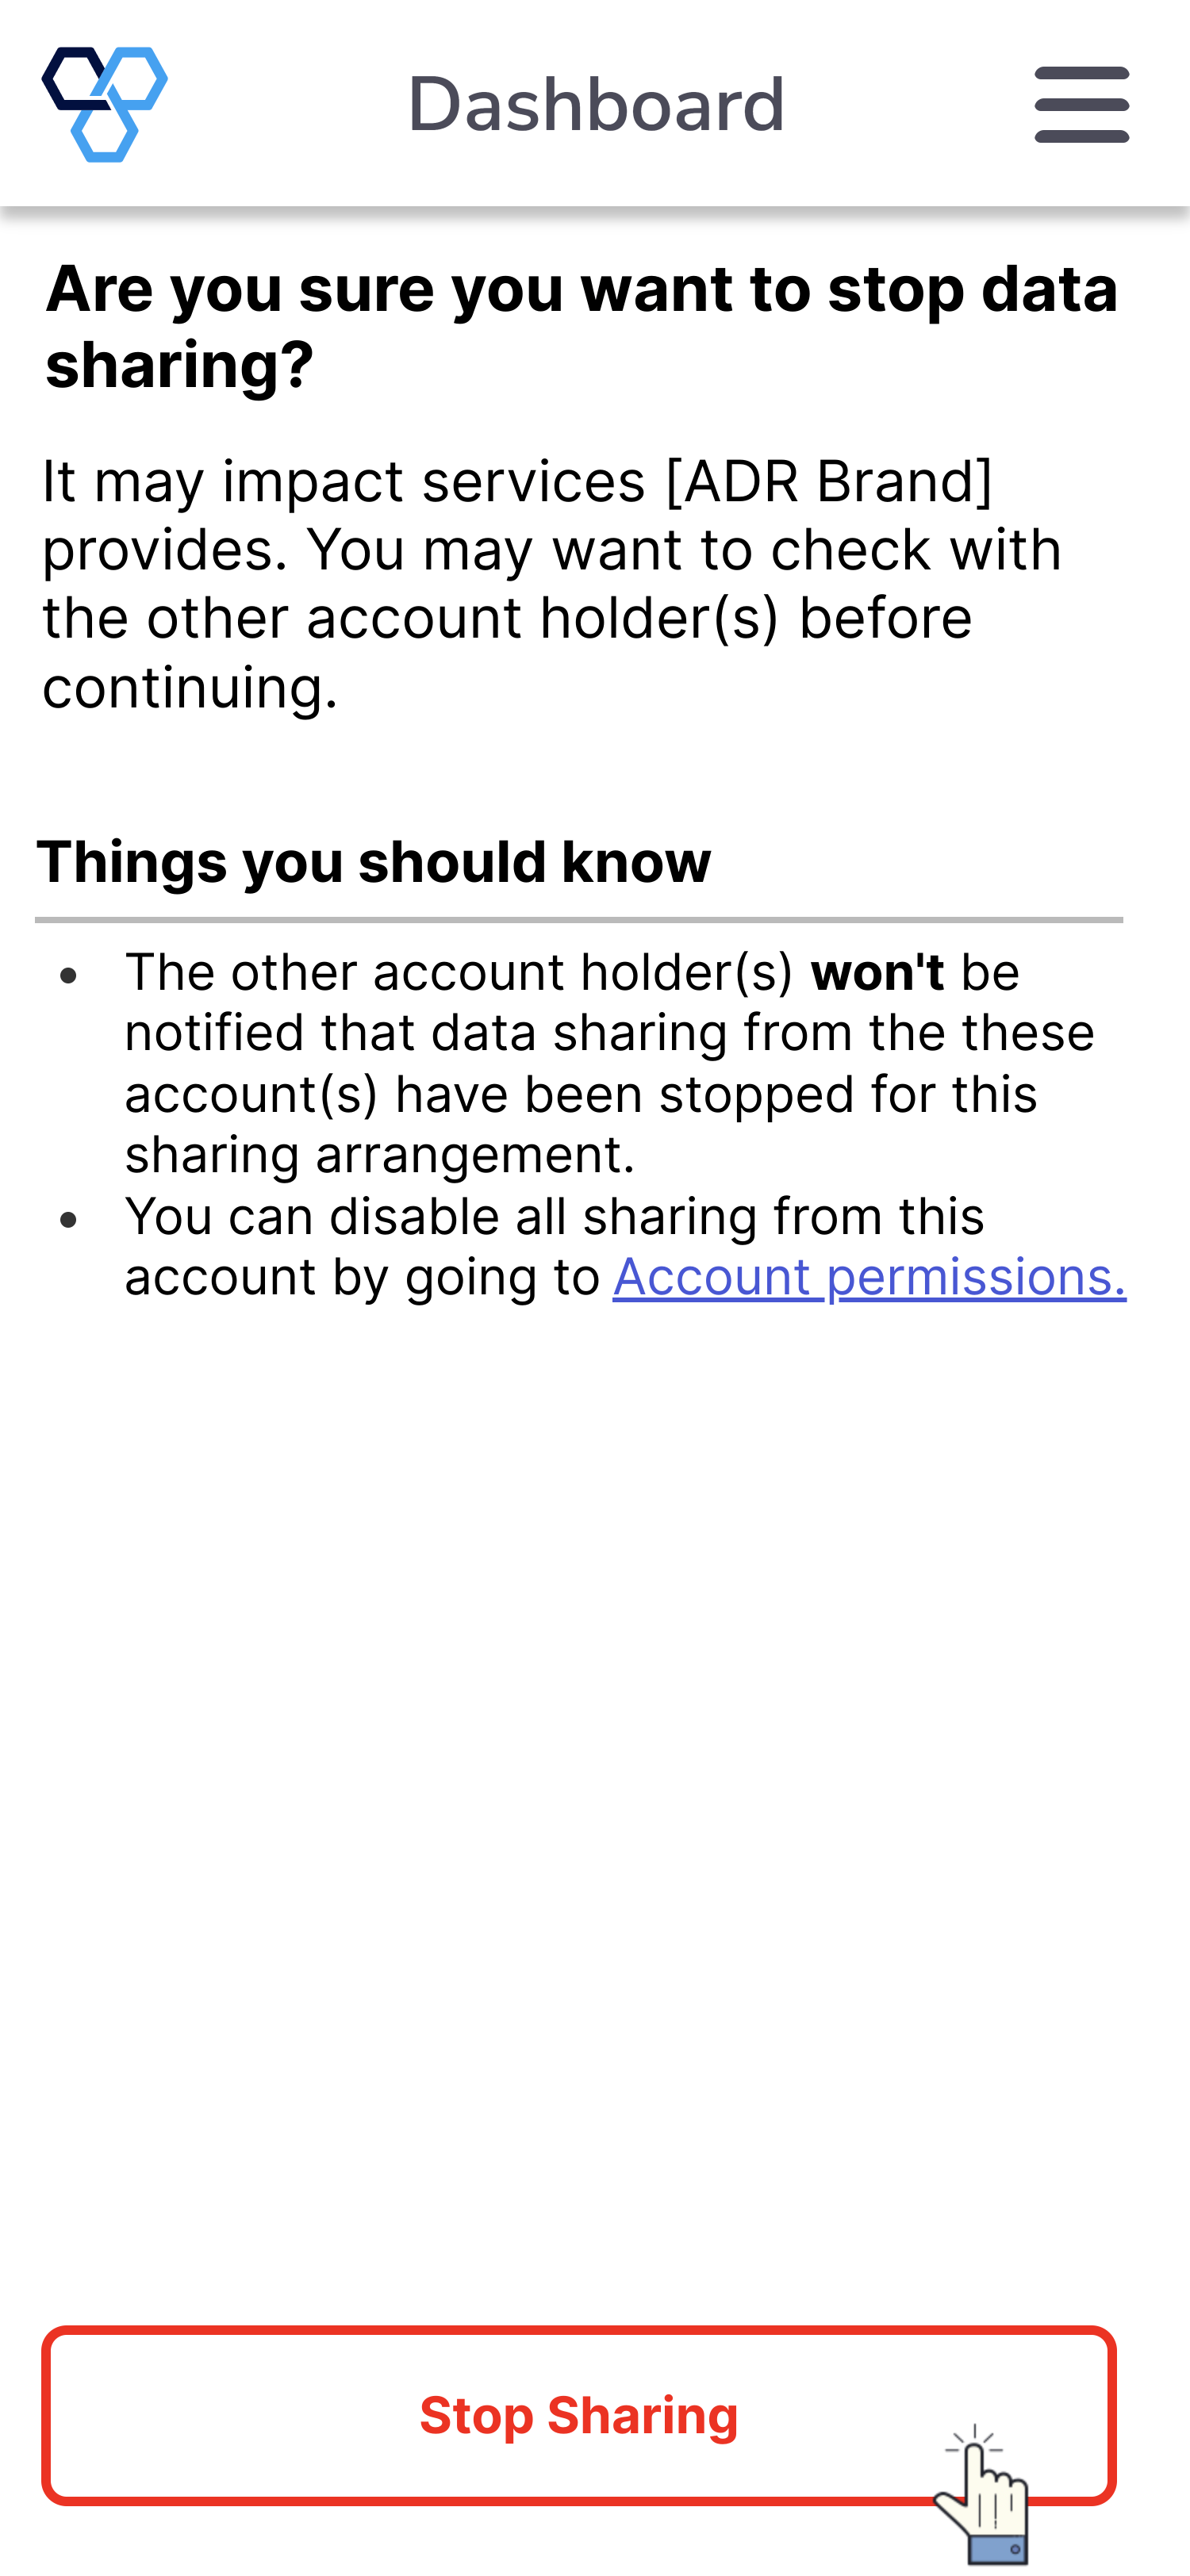
Initial Cancellation states notification won't be sent
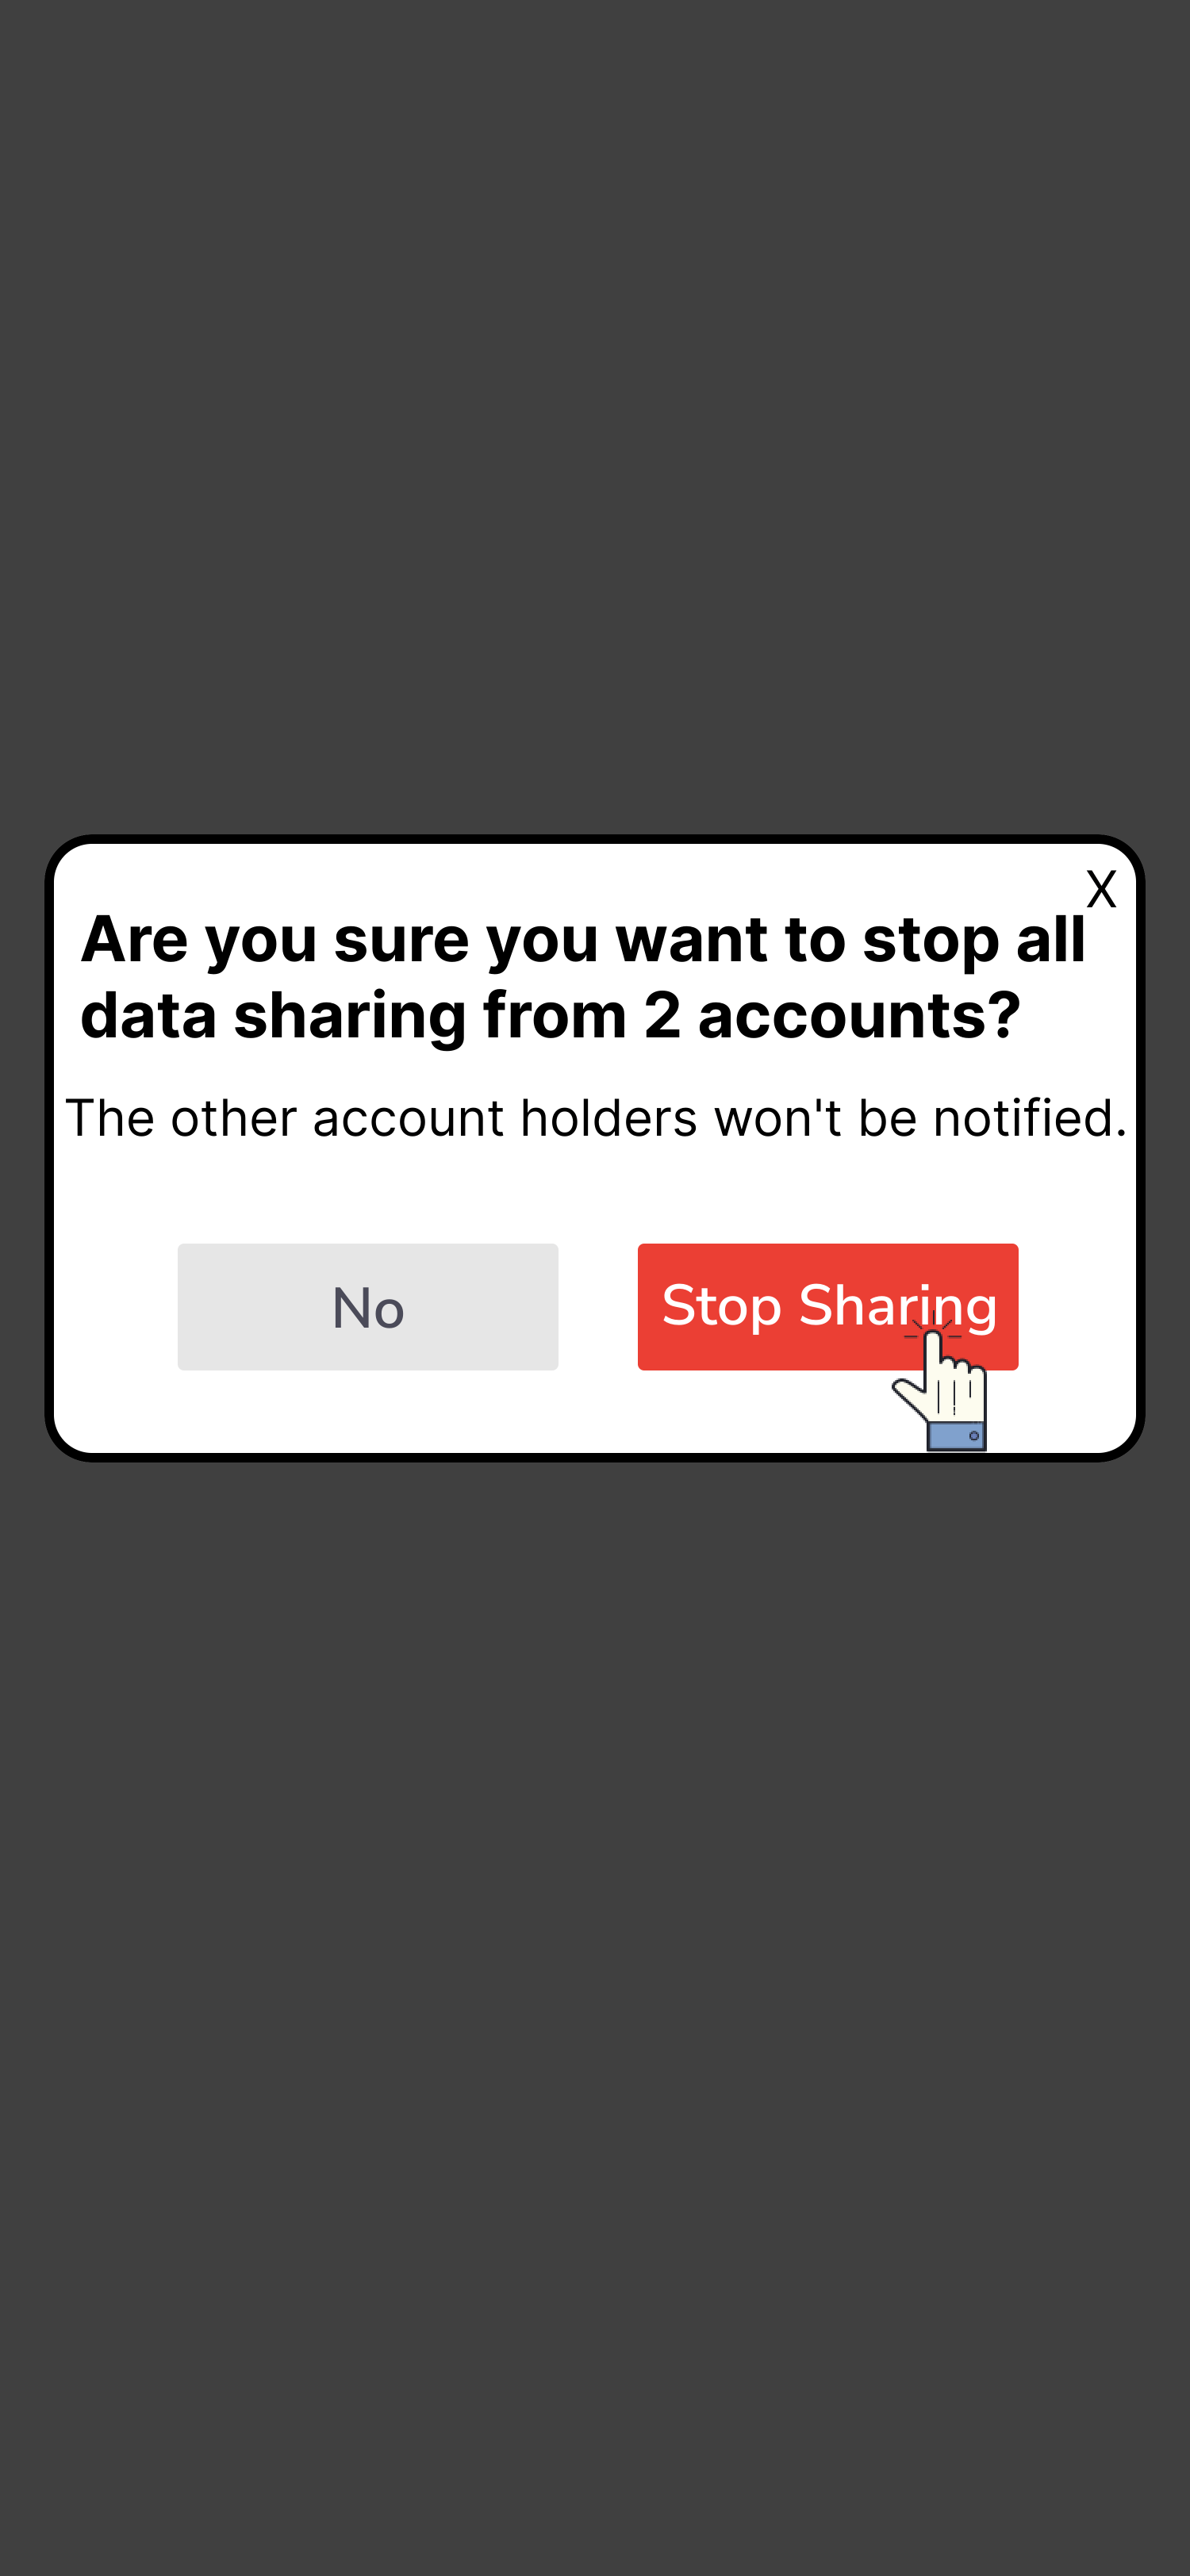
Confirmation again states they won't be sent
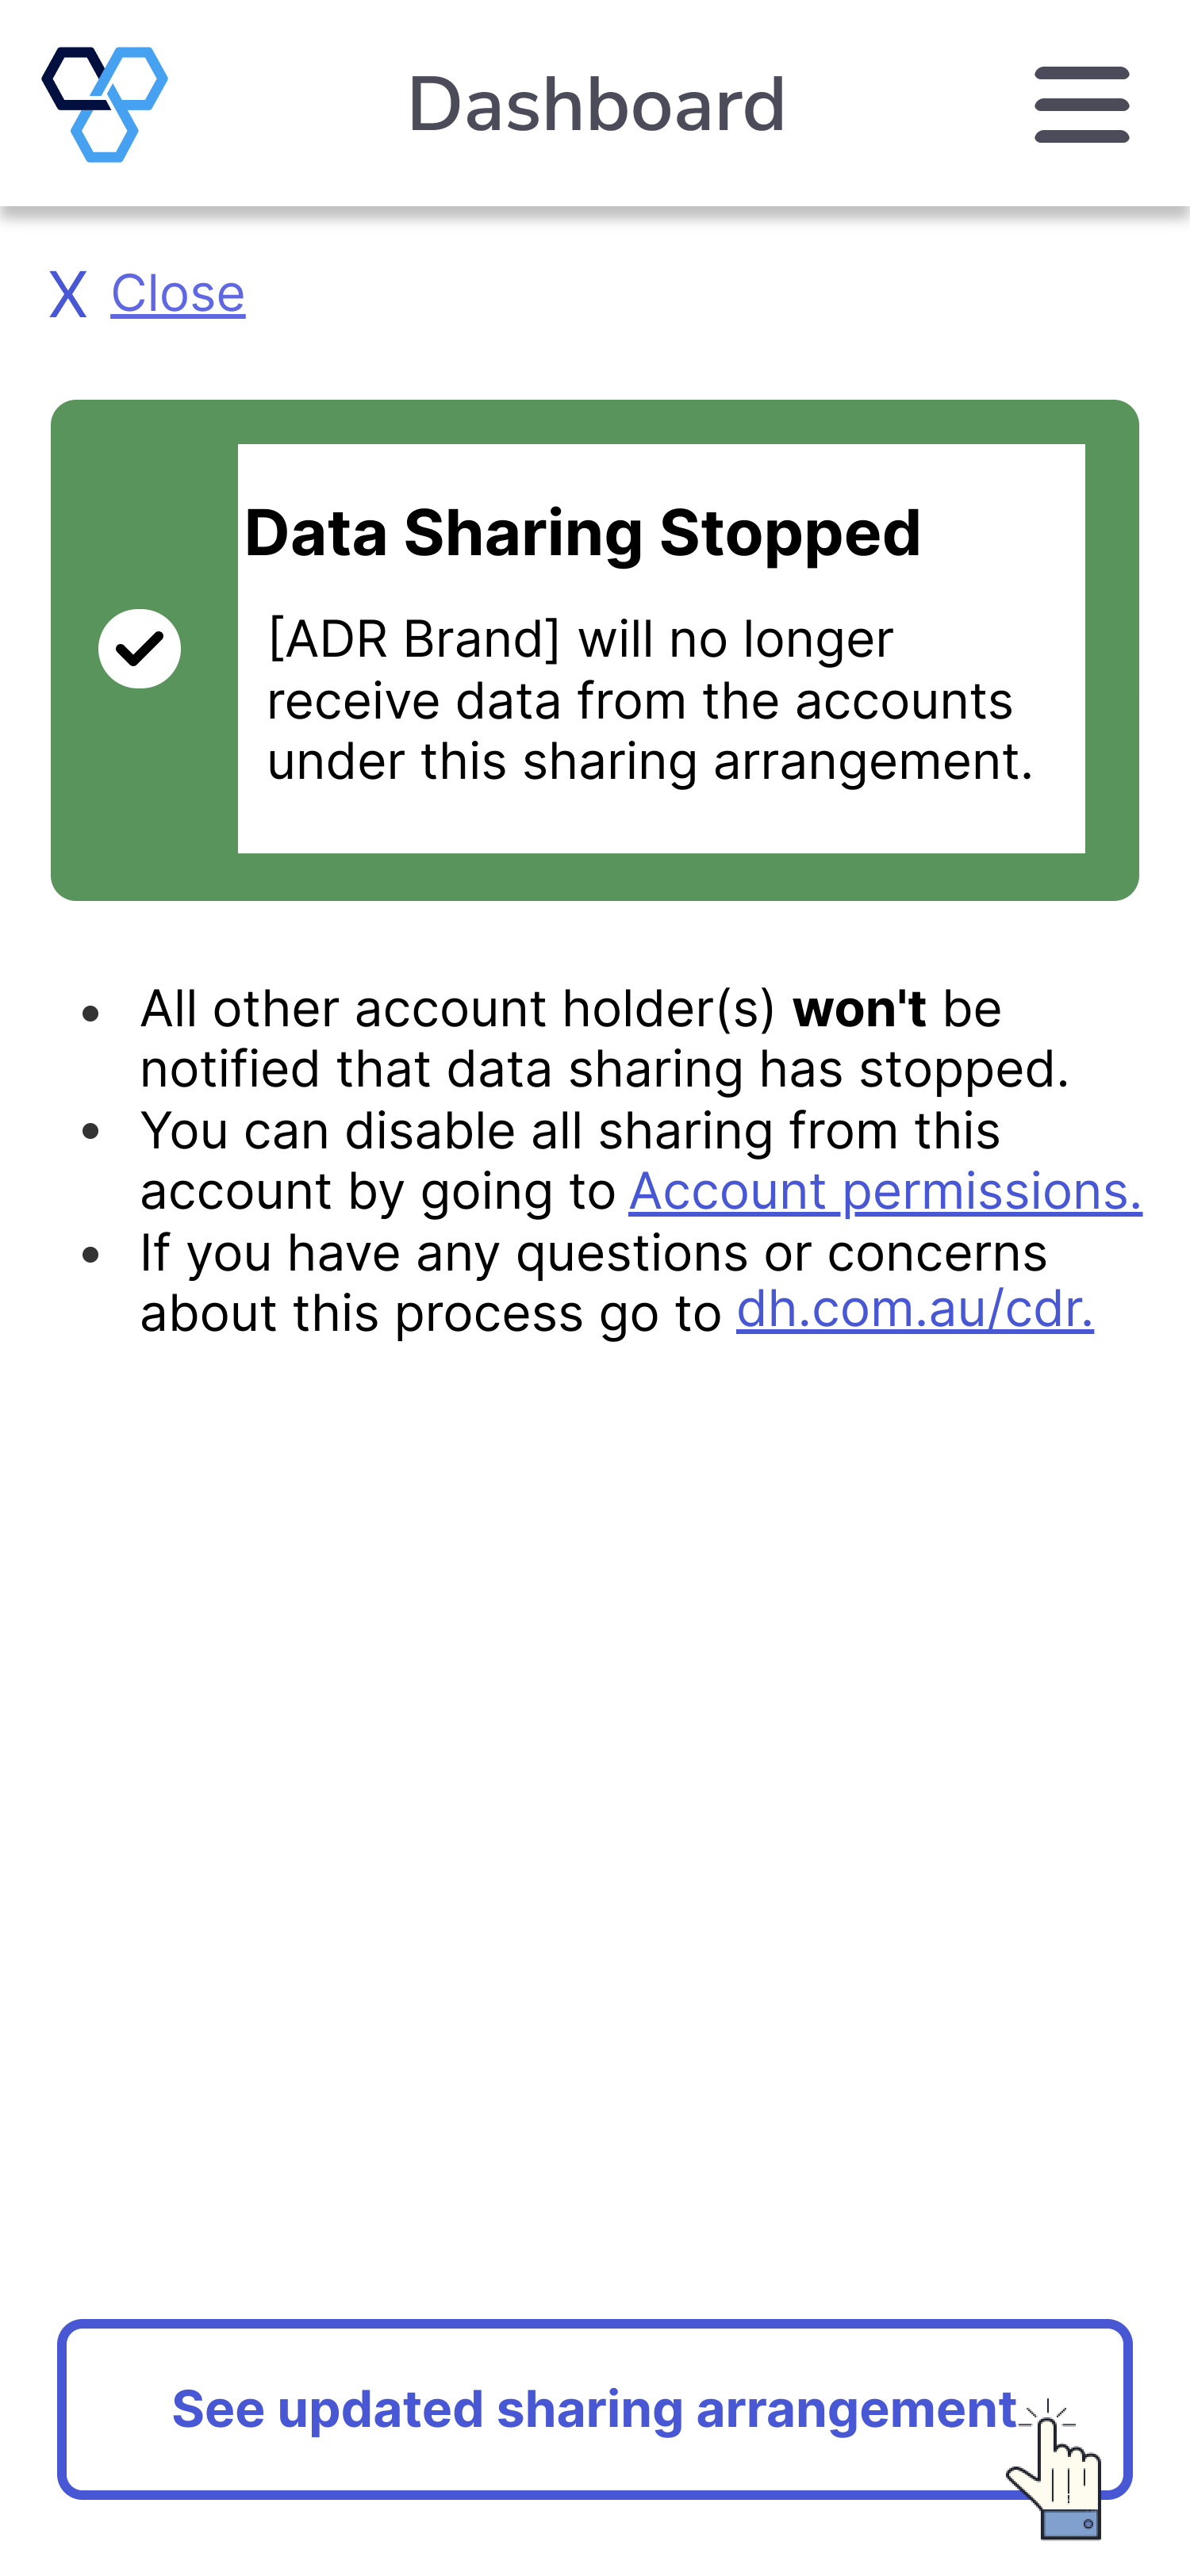
After cancellation the no notification message is affirmed again